Why this belongs on your roadmapFive outcomes leadership actually asks about — mapped to how the offering is delivered.

Zero Trust security
Enforce MFA, conditional access, and least-privilege across SAP and enterprise apps.

Lower operational cost
Eliminate password sprawl and cut helpdesk volume.

Faster transformation
Standardized identity for SAP RISE, BTP, and cloud adoption.

Workforce productivity
One login across Fiori, GUI, BTP, Cloud ALM, and beyond.

Audit-ready compliance
Centralized logging, MFA, and certificate governance from day one.
Built for the whole landscape, not one appThe same trust fabric spans SAP, Microsoft, and every SaaS app your users touch.
What changes in the first two quarters
80%
Reduction in authentication incidents
60%
Faster onboarding across SAP & SaaS users
99.9%
Authentication availability, HA design
100%
Audit readiness from day one
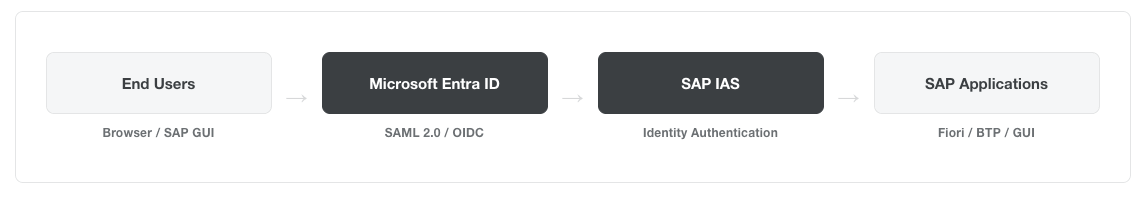
One trust path, every SAP entry pointA simplified view of the standard design — full reference architectures cover HA/DR, B2B/B2C, and hybrid cloud deployments.
Where does your organization sit today?
Most enterprises are somewhere between Level 2 and 3. The assessment tells you exactly where — and what closes the gap.
LEVEL 1Basic SSO
Password-based, manual provisioning, siloed identity.
LEVEL 2Federated SSO
SAML for Fiori, Entra ID as corporate IdP, basic MFA.
LEVEL 3Unified Identity
Full SAP + non-SAP SSO, automated provisioning.
LEVEL 4Adaptive Security
Risk-based MFA, conditional access, B2B federation.
LEVEL 5Zero Trust
Continuous verification, passkeys, AI-driven IAM.
Identity, delivered by SAP experts
Request your free SSO Maturity Assessment
We’ll map your current authentication landscape and show you where it stands on the 5-level maturity model, with no obligation to continue.
- Inventory of SAP & non-SAP apps and identity providers
- Gap and risk analysis against Zero Trust maturity
- Target architecture and phased roadmap